Saturday, October 24th 2026

ASUS Rushes Out Wi-Fi 7 Router Firmware Update to Fix Critical Vulnerability
ASUS rolled out an urgent security update for its latest Wi-Fi 7 router lineup, addressing an improper authentication vulnerability. The security flaw specifically affects router models currently running the 3.0.0.6_102 firmware series. According to the official ASUS security advisory, the bug allows an unauthenticated attacker situated on an adjacent network to completely bypass security protocols and gain full admin access to the router. While the "adjacent network" condition somewhat mitigates the threat by requiring the attacker to be in relative local proximity (rather than launching an attack entirely across the internet), the ability to compromise a network's central hub without requiring any credentials is a critical threat.
ASUS strongly recommends all affected users to download and install the newly patched firmware. You can fetch the necessary updates automatically through the router's built-in web administration portal or by manually downloading the firmware files directly from the official ASUS Support and Wi-Fi Router product pages. For network administrators unable to flash the new firmware right away, ASUS has outlined several temporary mitigations to minimize the attack surface. Most importantly, users must ensure that remote access from WAN is disabled, limiting management interface access exclusively to trusted local machines. ASUS also advises enforcing robust, unique administrator and Wi-Fi passwords. Users should aggressively monitor their networks to prevent untrusted devices from joining, review and wipe any unrecognized companion-app sessions, and perform a complete system reboot following any eventual firmware installation.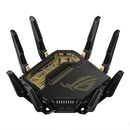
Source:
ASUS
ASUS strongly recommends all affected users to download and install the newly patched firmware. You can fetch the necessary updates automatically through the router's built-in web administration portal or by manually downloading the firmware files directly from the official ASUS Support and Wi-Fi Router product pages. For network administrators unable to flash the new firmware right away, ASUS has outlined several temporary mitigations to minimize the attack surface. Most importantly, users must ensure that remote access from WAN is disabled, limiting management interface access exclusively to trusted local machines. ASUS also advises enforcing robust, unique administrator and Wi-Fi passwords. Users should aggressively monitor their networks to prevent untrusted devices from joining, review and wipe any unrecognized companion-app sessions, and perform a complete system reboot following any eventual firmware installation.

34 Comments on ASUS Rushes Out Wi-Fi 7 Router Firmware Update to Fix Critical Vulnerability
Currently on it: 3.0.0.6_102 firmware series
.
Thanks GamerNexus.Vulnerability is still vulnerability. Better to be known and fixed than sitting there for ages.
I have had zero issues with the WAN throughput.
Also, why buy an Asus router if you're getting one that work with the Merlin firmware?Huh? He's supported most models for as long as it's been possible and nothing has been dropped after a year. Asus themselves support a lot or EOL models long after they stopped selling them, the only other consumer router manufacturer I've seen do that is Netgear.
And I will explain why since i'm using an Asus router with merlin firmware since about 2018 and I also have a cybersecurity background.
1. First issue using HTTP
They have purposely set it to HTTP instead of HTTPS which is what you should have been using for this "Attack"
2. Asus Mobile App is not a secure way to access the router. Using this app forces the router to Enable web access from WAN. Which means anybody port scanning from which ever country will be able to see your open port for this. Which is a major security NO NO. if you need to access your router remotely from outside that should be done via a vpn which you can setup inside the router.
3. What Cafe's can you go to that will have WIFI access and Random Ethernet ports open that you can just plug into?
4. The vulnerability requires an authenticated session if I already have this kind of access to your device you are already screwed.This is incorrect.
Models do not get dropped after a year. These 3 RT models are like 4 years old
Merlin also will updates components in the router before Asus does.
The most reason firmware just updated Open SSL to 3.5
Also taking months to fix a vulnerability also false if the issue has to be fixed up stream by ASUS and he has to wait.
Yes they have had many great videos but this video is just for views nothing else.
Proof of concepts can be important for researching security issues, but who cares about hypothetical attack vectors that could potentially be exploited.
Both things can be true at once.
Anything based on Linux, has bugs and security holes.
Also keep in mind that OpenWRT can't fix some things, unlike the router manufacturers, since they don't work directly with the chip makers.
As someone that has worked for a (now defunct) router manufacturer, I can tell you it's not easy to get them to address issues.
We found a bug that took MTK a good three months to issue a fix for and it was something pretty serious.
There's really no such thing as a secure router, no matter the manufacturer of the hardware or software.
I'm by no means dissing OpenWRT here, but I also don't think it's a good option for most consumers.
Routers have become extremely complex devices these days and maybe it's time to have a rethink as to how many features a router should have.
OpenWRT for the One is definitely more audited than any other consumer router and faster to get updates, and for the long term (to at least 2035, probably longer).
And Banana Pi is a two-bit outfit that are mostly clueless when it comes to router design, but ok...
And no, that's not the same as having an FAE you can call up and deal directly with.
As I said, I used to work for a router manufacturer and I have meet with all the router SoC manufacturers in the industry and I know how the operate.
MTK used to be terrible to deal with, but they seem to have changed their mind and appear to be want to be more opensauce friendly these days, which is nice.
That said, their turn around time (as mentioned) when there's an issue, wasn't great, but I guess they might've improved that too, but they're really a minor player in the market.
Even Qualcomm has lost market share, as most router makers seem to prefer Broadcom for some reason. If I could chose, I would use Qualcomm hardware, but that's often not a choice you can make as a consumer and at least from Asus side, they've been terrible at supporting anything that's not Broadcom.
Best router I ever had was my old Netgear R7800, which was Qualcomm based.And you make that assumption based on what exactly?
I mean, yeah, it'll most likely get OS updates for a long time, but not all OS updates add something useful for most people and updates can also break things.
I doubt it'll be supported for that long, as it's actually a rather terrible piece of hardware. Hopefully the second version will be better.
If I were to get an OpenWRT router today, it would be the GL.iNet GL-MT6000 Flint 2, as it does at least have decent hardware and a decent design.