Tuesday, February 10th 2026

Microsoft is Refreshing Secure Boot Certificates on Millions of Windows PCs

On your Windows PC, the Unified Extensible Firmware Interface (UEFI) firmware has a Secure Boot Certificate that mandates only verified software starts the boot-up sequence. Microsoft is preparing to refresh these certificates, and the company announced that millions of Windows PCs in circulation will receive new Secure Boot Certificates in an industry-wide gradual rollout to replace aging certificates that are expiring soon. According to the latest Windows Blog, the original Secure Boot Certificates introduced way back in 2011 are reaching the end of their planned lifecycle, with the expiration date set for late June 2026. This not only mandates updating but also requires a massive staged rollout from OEMs and Microsoft's partners to ensure that all Windows devices stay secure.

According to Microsoft, this is one of the largest industry collaborations that spans the Windows ecosystem, including servicing, firmware updates, and countless device configurations from OEMs and other hardware makers. Firmware makers are at the center with their UEFI BIOS patches, which will now have to replace their aging Secure Boot Certificates. The blog also states that OEMs have been provisioning updated certificates on their new devices, with some devices from 2024 and almost all PCs from 2025 updated to support the new certificate. Interestingly, older PCs and devices that were shipped prior to these years will also be taken care of, with major OEMs providing their own guidance on updating the certificate. If you don't see your OEM offering an update, be patient as the rollout is gradual.
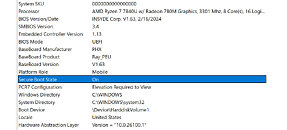
For those wondering what happens if you don't upgrade your certificate, the PC will continue to run just fine with no issues for now. However, Microsoft describes this as a "degraded security state," where PCs become prone to new boot-level security vulnerabilities. These vulnerabilities are discovered very often, and they can become a weak point for systems without new certification in place. Microsoft also notes that without new Secure Boot Certificates, systems may face compatibility issues as new hardware, software, and firmware that are Secure Boot-dependent may become a point of failure. Basically, the system may face corruption and won't continue to work in the future updates unless a new certificate is applied.
Source: Windows Blog
Add your own comment

65 Comments on Microsoft is Refreshing Secure Boot Certificates on Millions of Windows PCs

#26
lexluthermiester
R-T-BI know because my business utilizes this facility for our signed preboot environment. It IS a useful facility in such a context.
That's business. SecureBoot has no place in the consumer sector.
Posted on Reply
#27
Visible Noise
N3utroFyi if you want to check if your windows PC is already using the updated secure boot certificate use these commands in powershell:

([System.Text.Encoding]::ASCII.GetString((Get-SecureBootUEFI db).bytes) -match 'Windows UEFI CA 2023')

([System.Text.Encoding]::ASCII.GetString((Get-SecureBootUEFI dbdefault).bytes) -match 'Windows UEFI CA 2023')

They both return "true" if everything is OK.

From: www.dell.com/support/kbdoc/en-us/000385747/how-to-check-secure-boot-certificates
Only the first needs to return true. The UEFI NVRam has been updated with the new certificate.

The second will return true if the BIOS has been updated with the new certificate.
lexluthermiesterThat's business. SecureBoot has no place in the consumer sector.
I don’t like rootkits, but you do you.
Posted on Reply
#28
lexluthermiester
FR3D1You can claim a lot;
Yes, a claim backed up by extensive experience dealing with the problems that SecureBoot causes normal users with legitimate needs of functionality.
Visible NoiseI don’t like rootkits, but you do you.
Save that nonsense for the daffy minded nitwits..
Posted on Reply
#29
Visible Noise
lexluthermiesterSave that nonsense for the daffy minded nitwits..
You don’t think rootkits are a thing for everyone to be concerned about?

You should spend more time reading about technology security IMHO. Dan Goodin’s articles are a good place to start. For more advanced subjects there’s Brian Krebs.
Posted on Reply
#30
N3utro
lexluthermiesterThat's business. SecureBoot has no place in the consumer sector.
Without a reliable way to ensure the integrity of an operating system a virus that would exploit a vulnerable firmware (rootkit) or otherwise inject itself by another mean before the OS loads would be impossible to detect.

Viruses are not limited to businesses.
Visible NoiseOnly the first needs to return true.
@Visible Noise Nvram can be cleared during troubleshooting so it's a risk if the bios db hasn't been updated as well.
Posted on Reply
#31
azrael
So, Microsoft will push out an update on this for Windows 10? No? Another way to gently "nudge" people to please please please switch to Windows 11.

Another thing that's bothering me about this whole Secure Boot feature is that Microsoft sits with the keys and thus the leverage, even if you use Linux. They might just decide to block anything non-MS. In that case, you would have to switch off Secure Boot completely ...if you can. Not every firmware allows that.

EDIT: Just tried N3utro's two PS commands on my (updated) Windows 10 Pro. Both return false.
Posted on Reply
#32
TheDeeGee
Secure Boot is disabled by default on my ASRock Z590 Steel Legend.

And i play no games that require it, the only multiplayer game i play is Fortnite and that works without Secure Boot.
Posted on Reply
#33
Dragokar
TheDeeGeeSecure Boot is disabled by default on my ASRock Z590 Steel Legend.

And i play no games that require it, the only multiplayer game i play is Fortnite and that works without Secure Boot.
Below level 350 and outsides tournaments yes, we will if they update this in the long run.......
Posted on Reply
#34
TheinsanegamerN
Visible NoiseDo you understand why Microsoft will not sign GNU Grub2? Because under GPL 3, anyone - including your friends in governments around the world - can demand the signing key. Why on earth would you want that? Because Microsoft is “bad”?

Grub isn’t an OS anyway. You wouldn’t be able to answer the original question, would you?


Oh, I just saw your use of M$. I thought I was having a discussion of the facts with a mature adult. Nevermind.
Well perhaps Microsoft shouldnt have created a system where they have control of the keys and signing keys would expose them to governments, and thus the consumer is prevented from loading their own software instead of MicroSlop. That might be ANTI CONSUMER, which was the whole point. Hmmmmm....
lexluthermiesterThe whole concern is lacking and brainless.

SecureBoot is a worthless thing.
My solution to all this is to turn it off. I dont need it at home and enabling it forces me to make passwords for its access when setting up linux, among other headaches.
Posted on Reply
#35
TheDeeGee
DragokarBelow level 350 and outsides tournaments yes, we will if they update this in the long run.......
Yeh, i only play the original PvE Mode from before BR.
Posted on Reply
#37
Visible Noise
TheinsanegamerNWell perhaps Microsoft shouldnt have created a system where they have control of the keys and signing keys would expose them to governments, and thus the consumer is prevented from loading their own software instead of MicroSlop. That might be ANTI CONSUMER, which was the whole point. Hmmmmm....
Microsoft didn’t implement this by themselves. This is an industry standard across the entire PC ecosystem. That’s why the code is actually maintained by RedHat (IBM) - the Microsoft of Linux.
Posted on Reply
#38
lexluthermiester
Visible NoiseYou don’t think rootkits are a thing for everyone to be concerned about?
They are are not a problem for anyone using good antivirus/antimalware. SecureBoot does not outright stop RootKits either.
Visible NoiseYou should spend more time reading about technology security IMHO.
Gee, thanks for the tip. :rolleyes:
N3utroWithout a reliable way to ensure the integrity of an operating system a virus that would exploit a vulnerable firmware (rootkit) or otherwise inject itself by another mean before the OS loads would be impossible to detect.

Viruses are not limited to businesses.
There are lots of ways for criminals to do hacker things. SecureBoot doesn't stop anything in that area. SecureBoot does very little to prevent anything.
TheinsanegamerNMy solution to all this is to turn it off.
Same here. My security methodology covers all the bases.
Posted on Reply
#39
Easo
R-T-BI don't know, we should probably see how well the rollout actually goes before declaring anything either way.
So far doing tests at my work it seems it as long as your BIOS is not too outdated PC's are ready for the switch. And as per latest material it does not mean your PC won't boot after it expires which was something that was not clear - now this is something MS should work on, learn.microsoft.com tends to have unclear information from time to time.
Posted on Reply
#40
Dr. Dro
AleksandarKMicrosoft also notes that without new Secure Boot Certificates, systems may face compatibility issues as new hardware, software, and firmware that are Secure Boot-dependent may become a point of failure. Basically, the system may face corruption and won't continue to work in the future updates unless a new certificate is applied.
Wonder if this is where they'll finally start enforcing the whole "minimum system requirements" lunacy they came up with.


Because y'know. A 22C/44T workstation CPU just isn't enough to run Windows. What we all need to do is tell Microsoft to simply go where the sun don't shine.
Posted on Reply
#41
N3utro
lexluthermiesterThere are lots of ways for criminals to do hacker things. SecureBoot doesn't stop anything in that area. SecureBoot does very little to prevent anything.
If it doesn't stop anything as you say, how do you explain that the most popular OSes have all implemented it and in most cases also did things to strongly enforce it as well?

Windows, android, ios, macos, ubuntu, debian, redhat, arch... They are all managed by security experts independent from each others, yet they all chose to implement it.

Implementing security features isn't something easy to do, it's a lot of work and testing, so it costs a lot of money. Do you really think they would all agree to spend on this feature if it wouldn't "stop anything in that area" or "does very little to prevent anything" as you say?

Do you really think you know better about this than multiple security professionals who have feedback on billions of devices around the world?
azraelSo, Microsoft will push out an update on this for Windows 10? No? Another way to gently "nudge" people to please please please switch to Windows 11.

Another thing that's bothering me about this whole Secure Boot feature is that Microsoft sits with the keys and thus the leverage, even if you use Linux. They might just decide to block anything non-MS. In that case, you would have to switch off Secure Boot completely ...if you can. Not every firmware allows that.

EDIT: Just tried N3utro's two PS commands on my (updated) Windows 10 Pro. Both return false.
Windows 10 extended support will end more or less at the same time (october 2026) than when the old secure boot certificate will start to expire (mid 2026) so it doesn't change much in that regard anyway.

Also secure boot can work with any keys. Linux distributions use the MS ones by default because it's easier as motherboard manufacturers implement them to work with windows, but you can install any keys from any source you want. On android devices each manufacturer use their own keys for secure boot to verify the OS integrity when it's running. So no, secure boot wouldn't be unusable on other OSes even if MS somehow decided to make the usage of their keys exclusive.

Anyway windows 10 and 11 experience is roughly the same so i don't really understand why would people chose to stay on 10 when 11 has more up to date features so across the board things work better on it.

I reinstalled win11 four months ago on my pc to make a clean switch to 25H2, i haven't had a single crash or issue on it since then, it works flawlessly. I opted out from the AI and cloud features when installing and haven't been bothered with them as well.
Posted on Reply
#42
Dr. Dro
N3utroDo you really think you know better about this than multiple security professionals who have feedback on billions of devices around the world?
Lex really isn't wrong on his points here. Secure Boot's purpose is to simply ensure kernel integrity during the boot process. When Secure Boot is set up and in the "User" state, it will halt the initialization process if an unauthorized UEFI extension/driver or bootloader is detected by the firmware. On paper, verifying the digital signature should stop a compromised kernel or bootloader dead in its tracks, but of course, there are ways around it and very high severity exploits that virtually negate any and all benefits from Secure Boot, which makes it in practice, a formality.

Some security and anti-tamper software request Secure Boot support as a form of insurance that the OS is booting unmodified, or in this case, only affected by the software in question. It is not a technical limitation, if you think about it, many such applications are designed like and essentially function the same way as rootkit malware, a few examples are anti-tamper protection software some banks demand to allow access to internet banking services (many infamous for annihilating system performance and being active even when such websites are not being browsed), or particularly aggressive types of anti-cheat systems like Riot Vanguard, which is known to write directly into your system's EFI partition.
Posted on Reply
#43
FR3D1
Ninja Cat
OnasiCut out that patronizing bullshit.
Very thin ice.
OnasiAgain - if this rollout will necessitate manual BIOS updates from a large portion of users it WILL be a shitshow.
I previously thought you were someone with a certain level of expertise. However, in hindsight, this seems to have been a mistake. My source was more than clear enough that a firmware update would not be an option for most people. And even if that had been the case, purely hypothetically speaking, do you really think your fellow human beings are incapable of doing anything more than swiping from right to left? Then there are two of us! But let's be honest, nowadays, and not just since yesterday, no one needs to create a bootable stick, boot into a DOS environment, and use the command line to update their BIOS. Even the “dumbest assumable user,” or DAU for short, would be able to update their BIOS with the newfangled methods. Not to mention the fact that most systems even have a dual BIOS with recovery if necessary. By the way, I have successfully updated many a (V)BIOS blindly. Always successfully. So much for my expertise.
lexluthermiesterwith the problems that SecureBoot causes normal users with legitimate needs of functionality.
Who, for example? I don't know any personally. Not even in my circle of acquaintances, where I maintain all the systems.
azraelSo, Microsoft will push out an update on this for Windows 10?
  • [Secure Boot] With this update, Windows quality updates include a broad set of targeting data that identifies devices and their ability to receive new Secure Boot certificates. Devices will receive the new certificates only after they show sufficient successful update signals, which helps ensures a safe and phased rollout.
Source
TheDeeGeeAnd i play no games that require it
With that attitude, you're doing everything right. Not.
lexluthermiesterSecureBoot does very little to prevent anything.
Insane. Truly!
N3utroso across the board things work better on it.
That's not entirely correct, and you know it.

With a friendly smile,
Fred.
Posted on Reply
#44
lexluthermiester
FR3D1Who, for example? I don't know any personally. Not even in my circle of acquaintances, where I maintain all the systems.
Yeah, I'm going to fall for that bait..
FR3D1Insane. Truly!
No, FACT! And if you had been working tech and IT as long as I have you would know this.
Posted on Reply
#45
R-T-B
Visible Noise:roll:
Not really funny but yeah, no politics anyways.
lexluthermiesterThat's business. SecureBoot has no place in the consumer sector.
I disagree, respectfully. It just needs to be a clear choice and either way that's not really happening so we are on the same team, anyways.
Posted on Reply
#46
N3utro
lexluthermiesterNo, FACT! And if you had been working tech and IT as long as I have you would know this.
I've been working in IT for over 20 years, managed a lot of PCs in very secure environments (banking, corporate trade secrets...). The fact that you recommend the general public to not use secure boot from my point of view is a disgrace to our profession. You're endangering the security of other people. It's like if a car vendor would say to their buyer "dont use the seatbelts".
Posted on Reply
#48
lexluthermiester
N3utroThe fact that you recommend the general public to not use secure boot from my point of view is a disgrace to our profession.
That only means you do not understand the consumer market and/or proper security methodologies. That speaks volumes. I would never trust such a school of thought in any way. Hardware security measures are no better than software security measures. And both restrict end user liberties to run and configure their own device as THEY see fit. The difference is that with software, something the end user doesn't want can be easily disabled/removed/replaced and that liberty & freedom should ALWAYS be present, regardless of what someone who subscribes to the "SecureBoot/TPM" school of thought believes is "right". I find such things detestable and, in a way, evil.
N3utroYou're endangering the security of other people.
This is complete moose muffins and mostly myth. Pull the other one.
N3utroIt's like if a car vendor would say to their buyer "dont use the seatbelts".
No it isn't. Such an analogy is as vapid as microsoft competence in creating stable updates.
Posted on Reply
#49
N3utro
lexluthermiesterThat only means you do not understand the consumer market and/or proper security methodologies. That speaks volumes. I would never trust such a school of thought in any way. Hardware security measures are no better than software security measures. And both restrict end user liberties to run and configure their own device as THEY see fit. The difference is that with software, something the end user doesn't want can be easily disabled/removed/replaced and that liberty & freedom should ALWAYS be present, regardless of what someone who subscribes to the "SecureBoot/TPM" way school of thought believes is "right". I find such things detestable and, in a way, evil.

This is complete moose muffins and mostly myth. Pull the other one.

No it isn't. Such an analogy is as vapid as microsoft competence in creating stable updates.
Secure boot doesn't restrict the liberty to run anything, it just makes sure that what you have decided to boot on has not been tampered with.

It's like if you had a food tester in a restaurant who would try your food before you eat to see if it had been poisoned. You can still choose any food you want, even make your own food and select your own food taster.

It seems like you have no idea of how it really work or you wouldn't say such things.

Anyway it feels like even if we gave you the perfect, irrefutable argument you still wouldn't accept it. As we say in France, "there are no deafer people than the ones who don't want to hear".

So i'm gonna stop wasting my time hitting on a wall.
Posted on Reply
#50
lexluthermiester
N3utroSecure boot doesn't restrict the liberty to run anything, it just makes sure that what you have decided to boot on has not been tampered with.
Oh please. Don't talk like you think I'm a noob idiot that knows nothing. SecureBoot is expressly designed to prevent the booting of any software that does not have properly signed bit-streams. It makes a lot of things a royal PITA, and no I'm not running down that list. If you don't understand what is at play, that's on you.
N3utroIt's like if you had a food tester in a restaurant who would try your food before you eat to see if it had been poisoned. You can still choose any food you want, even make your own food and select your own food taster.
You can stop with the analogies that do not fit the context of this discussion.
N3utroIt seems like you have no idea of how it really work or you wouldn't say such things.
Irony! Far out.
N3utroSo i'm gonna stop wasting my time hitting on a wall.
THAT is the most intelligent thing you've stated thus far. Move along..
Posted on Reply
Add your own comment
Nov 20th, 2026 15:59 PST change timezone

New Forum Posts

Popular Reviews

TPU on YouTube

Controversial News Posts